 Fastero Dev Team
Pasting an API key into a notebook cell is the fastest way to leak it: notebooks get shared, copied to GitHub and printed into outputs. Colab has had a better place for keys since November 2023, when it "Launched Secrets, for safe storage of private keys on Colab". This guide covers how Colab's secrets work, the three errors you'll meet, a limit few guides mention, and what to do with keys a whole team needs.
The short answer: open the key icon in Colab's left sidebar, add a secret with a name and a value, and switch on Notebook access for the notebook that needs it. Then read it in code with from google.colab import userdata and userdata.get("NAME"), which returns the value as a string. Secrets belong to your Google account, not to the notebook: anyone you share the notebook with gets your code but not your keys. If userdata.get fails, the secret doesn't exist under that exact name, the notebook hasn't been given access, or the code isn't running from the Colab interface, where secrets "can only be fetched".
Fastero
Jupyter notebooks for your team, with nothing to install.
Start a notebook or bring your .ipynb files. SQL cells query your databases with no password in the code, and a notebook runs now or on a schedule. Colleagues open it with their own login; viewers are free.
Try free →How Colab secrets work
- Open the Secrets panel from the key icon in the left sidebar of a notebook.
- Add a new secret: a name, such as
OPENAI_API_KEY, and its value. Names can't contain spaces. - Switch on Notebook access for the notebook you're in. The list of secrets is "global and visible in all your notebooks", but each notebook gets a secret only when you switch access on for it.
- Read it in code:
from google.colab import userdata

api_key = userdata.get("OPENAI_API_KEY")
The value comes back as a string, so convert a number yourself. Many libraries read keys from environment variables, so a common next line is:
import os

os.environ["OPENAI_API_KEY"] = userdata.get("OPENAI_API_KEY")
Since 2024, the panel also creates and imports Gemini API keys from Google AI Studio directly into your secrets.
The errors, and what they mean
All three come from Colab's userdata module, whose source is public:
SecretNotFoundError: Secret OPENAI_API_KEY does not exist. No secret has that exact name. Names are case-sensitive, so check the spelling against the panel; if you just created it, run the cell again.
NotebookAccessError: Notebook does not have access to secret OPENAI_API_KEY The secret exists, but Notebook access is off for this notebook. Switch it on in the panel. Colab can also ask with a pop-up the first time code requests a secret; if you refused it, libraries such as Hugging Face's tell you to restart the session to be asked again.
TimeoutException: Requesting secret OPENAI_API_KEY timed out. Secrets can only be fetched when running from the Colab UI. The request for the secret got no answer within 10 seconds, which the code says usually means the notebook is "being run from an export where the Colab UI is not available."
Two smaller ones: ValueError: Secret name cannot contain spaces or whitespace, and ModuleNotFoundError: No module named 'google.colab' when you run the same notebook outside Colab, where the google.colab package doesn't exist.
Where secrets stop working
That last error points at the limit worth planning around: Colab secrets are fetched by the Colab interface you have open. They work while you run cells in Colab, and they don't travel with the notebook:
- Run it in Jupyter, VS Code or a scheduler and
google.colabisn't there; read keys from environment variables instead. - Share it, or a colleague copies it, and they get none of your secrets. "Your secrets are only accessible to you and the notebooks you choose", so each person has to add their own under the same names.
- Schedule it and there's nothing to schedule: consumer Colab switched scheduled notebooks off on 27 March 2026.
A pattern that works in both places reads the environment first and falls back to Colab:
import os

def get_secret(name):
    if name in os.environ:
        return os.environ[name]
    from google.colab import userdata  # only exists in Colab
    return userdata.get(name)

db_url = get_secret("DATABASE_URL")
Jupyter notebooks for your team.
Start free →Keeping keys out of shared notebooks
Secrets keep keys out of your code, but a notebook can still leak them in other ways:
- Never print a secret. Cell outputs are saved in the notebook file, and anyone you share it with, or anyone who sees it on GitHub, can read them.
- Watch the copy button. Pressing Copy value in the panel shows the value on screen, so not during a screen share or recording.
- Grant access only where needed. Notebook access is per notebook; a notebook you share widely should have as few secrets as possible.
- Keep Colab's AI in mind. By default "Colab AI does not have access to your Google Drive files or user secrets", but it "can generate code that accesses them at your explicit request", and in consumer Colab, Google keeps prompts and related code to improve its products. See our Colab AI guide.
- Clear outputs before committing a notebook to Git, with
nbstripoutorjupyter nbconvert --clear-output.
Secrets for a team's notebooks
Colab secrets are personal: one person, one Google account, one set of keys, fetched while that person has the notebook open. A team's notebook that reads the company database every morning needs the opposite: one place for the credential, used by the notebook when it runs on its own, and colleagues who can run it without ever holding the password.
In Fastero, an AI and data platform where people and AI agents work together on a team's data, that's how notebooks get their credentials:
- Secrets live in the workspace, for the organisation or a project, and reach notebook cells as environment variables, in interactive and scheduled runs alike, so
os.environ["DATABASE_URL"]works on a schedule too. - SQL cells don't need one at all: they query a workspace connection whose credentials stay in the workspace, and hand the rows to Python as a pandas DataFrame.
- Schedules on the Free plan: run a notebook on any cron schedule, with no browser open.
- Sharing with a sign-in: colleagues open the notebook with their own login, and viewers are free.
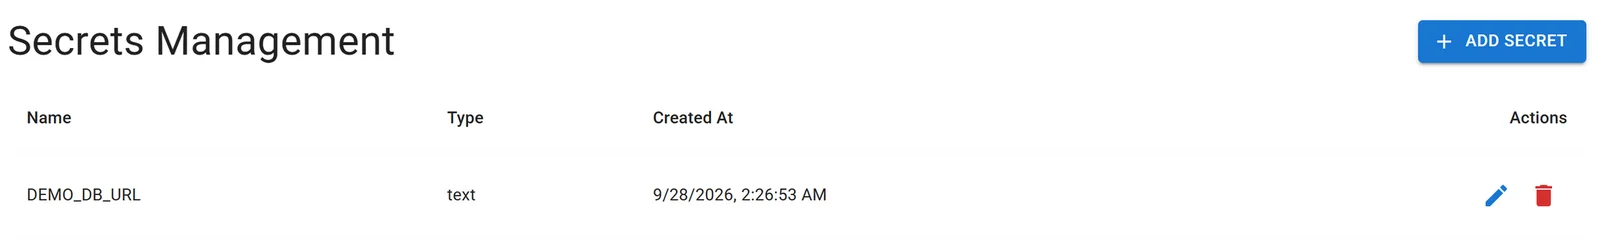
Workspace secrets in Fastero: notebooks and Python jobs read them as environment variables. Sample data.
The get_secret function above works unchanged in a Fastero notebook, where the value comes from the environment. More on Colab alternatives and sharing a Jupyter notebook.
FAQ
How do I use secrets in Google Colab?
Click the key icon in the left sidebar, add a secret with a name and value, switch on Notebook access, then read it with from google.colab import userdata and userdata.get("NAME").
Are Colab secrets shared when I share a notebook?
No. Secrets belong to your Google account. People you share a notebook with get the code, and need to add their own secrets under the same names.
Why does userdata.get say the notebook doesn't have access?
Notebook access is switched off for that secret in this notebook. Switch it on in the Secrets panel; if you refused Colab's pop-up asking for access, restart the session to be asked again.
Why does userdata.get say the secret does not exist?
There's no secret with that exact, case-sensitive name in your Secrets panel. Check the spelling, or add it.
Can I use Colab secrets outside Colab?
No. google.colab.userdata only works when running from the Colab interface; elsewhere the module is missing or the request times out. Use environment variables, with a fallback to userdata inside Colab.
Can I rename a Colab secret?
Guides that walk through the panel say you can change a secret's value but not its name: add a new secret instead and delete the old one.
Are Colab secrets secure?
They keep keys out of your code and out of copies you share. They don't stop a key leaking through a printed output, a screen share, or code that sends it somewhere, so treat outputs and AI prompts with care.
Sources
Read on 6 November 2026:
- Google — Colab release notes, Colab FAQ,
google.colab.userdatasource, Deprecation notice of scheduled notebooks (27 March 2026) - Hugging Face —
huggingface_hubtoken handling in Colab - Guides — Secrets in Google Colab (Thinktecture Labs), Notebook secrets in Google Colab (Python for Finance course notes)
Try Fastero free — keep your team's keys in one workspace and run notebooks on a schedule with them, no browser open. No credit card required.